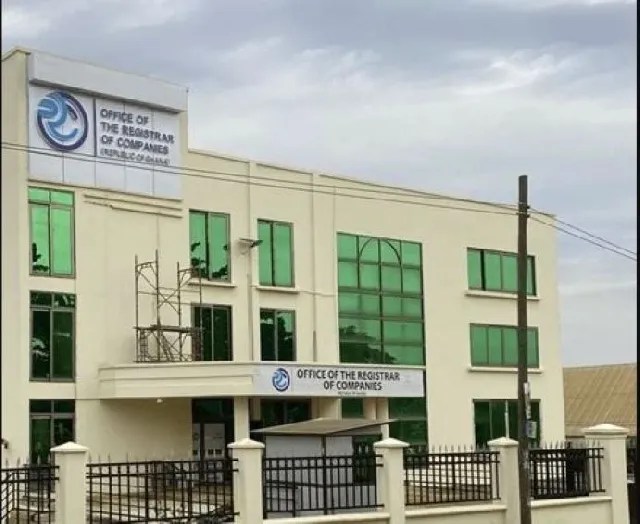
The recent fine imposed on the Office of the Registrar of Companies (ORC) and Purpleline Solutions Limited by the Cyber Security Authority (CSA) highlights a critical issue in Ghana's cybersecurity landscape. This incident underscores the importance of adhering to regulatory requirements and the potential consequences for non-compliance.
A Tale of Unlicensed Cybersecurity
In my opinion, this case serves as a stark reminder that engaging unlicensed cybersecurity providers can have severe repercussions. The ORC's failure to comply with the CSA's directives, which mandated the use of licensed Cybersecurity Service Providers (CSPs), led to a substantial fine. The ORC was fined GH¢240,000 for each of the two instances of non-compliance, totaling GH¢480,000. This financial penalty is a significant reminder of the importance of adhering to cybersecurity regulations.
What makes this particularly fascinating is the involvement of Purpleline Solutions Limited. The company was fined GH¢120,000 for providing cybersecurity services without the necessary license. This highlights a common misconception: applying for a license is not the same as holding one. Entities must obtain the requisite license before commencing regulated cybersecurity operations.
The Broader Implications
This incident raises a deeper question about the responsibility of organizations in safeguarding critical information infrastructure. The CSA's statement emphasizes that cybersecurity licensing is a legal requirement, not an administrative formality. This means that organizations entrusted with sensitive data and critical systems must take their cybersecurity obligations seriously.
One thing that immediately stands out is the CSA's proactive approach to monitoring compliance. The authority has directed designated Critical Information Infrastructure institutions, public-sector organizations, and other entities to verify the licensing status and appropriate license tier of cybersecurity service providers before awarding contracts or allowing them to commence work. This demonstrates a commitment to ensuring that only qualified and licensed providers are engaged.
Looking Ahead
As the cybersecurity landscape continues to evolve, it is crucial for organizations to stay informed about regulatory changes and best practices. The CSA's actions send a clear message that non-compliance will not be tolerated. Organizations must take a step back and consider the potential risks associated with engaging unlicensed providers. By prioritizing cybersecurity and adhering to regulatory requirements, organizations can better protect their critical systems and sensitive information.
In my view, this incident serves as a valuable lesson for all stakeholders involved in Ghana's cybersecurity ecosystem. It highlights the importance of collaboration between regulatory bodies, organizations, and service providers to ensure a robust and secure digital environment.